AI-Driven Automated
Security Testing
Traditional automated tools lack human intuition, forcing teams to rely on slow, manual workflows. Zarb bridges that gap, delivering security testing that thinks, adapts, and tests like a human, all at machine speed.
Objective
Find out what 192.0.2.25 exposes to the internet and how it lets people sign in. Do not exploit anything you find.
Planned steps
-
1
nmap -Pn -sV -p- 192.0.2.25 -
2
nmap -Pn -sC -sV -p 22,80,443 192.0.2.25 -
3
curl -kIs https://192.0.2.25/ -
4
ffuf -u https://192.0.2.25/FUZZ -w common.txt
Missions pause here for your review, and the remaining plan adapts as output comes back.
Testing runs securely from a dedicated environment for your organization
Every finding is traceable to the exact command and output that produced it
Every report clearly states what was covered and what could not be reached
Ask for What You Need in Plain English
Zarb translates a natural-language request into a complete testing methodology. No command syntax, tool configuration, or prior security experience required.
Web application scan
Check my online store at shop.example.com for security risks and give me a report in plain English. Tell me what is at risk and what I should fix first.
What Zarb delivers
Zarb automatically generates reports that deliver actionable remediation steps for technical teams and strategic risk insights for executive leadership. Both download as PDFs.
Web application scan, signed in
We have a PCI audit coming up. Test the customer login and dashboard with this test account and tell me in plain terms what is wrong and what to fix first.
What Zarb delivers
Zarb runs the same tests from an authenticated perspective using credentials you provide, and returns the same reports with what was (and was not) covered.
Network scan
One of our office servers is at 192.0.2.25. Check what is exposed to the outside and whether an attacker could use any of it. Do not change anything or cause an outage.
What Zarb delivers
Zarb maps every reachable port and service, highlights exposed data, and shows what to fix first. Testing is non-destructive and never includes Denial of Service (DoS) attacks.
The Console
The console is where every assessment is configured, monitored, and reviewed. Zarb supports single missions, repeatable scans, and campaigns that chain several missions together, all managed from one place.


How an Assessment Runs
-
01
The objective is planned
Write a mission objective, define a campaign, or select a scan methodology. Missions pause for your review before execution, while scans proceed automatically once planning is complete.
-
02
The plan executes against the target
Commands run on the Alpha. After each step completes, the agent analyzes the output and can add new steps, retire ones that no longer apply, or reorder what remains.
-
03
The record builds as it runs
Findings are recorded and revised while the assessment is still running rather than reconstructed at the end. Reports are generated from those stored step analyses and the evidence behind them.
Full Visibility Into Every Step
Zarb records every step as it executes, capturing the command, the reasoning behind it, the raw output, and the resulting analysis. You can follow the assessment live rather than waiting for a final report to tell you what happened.
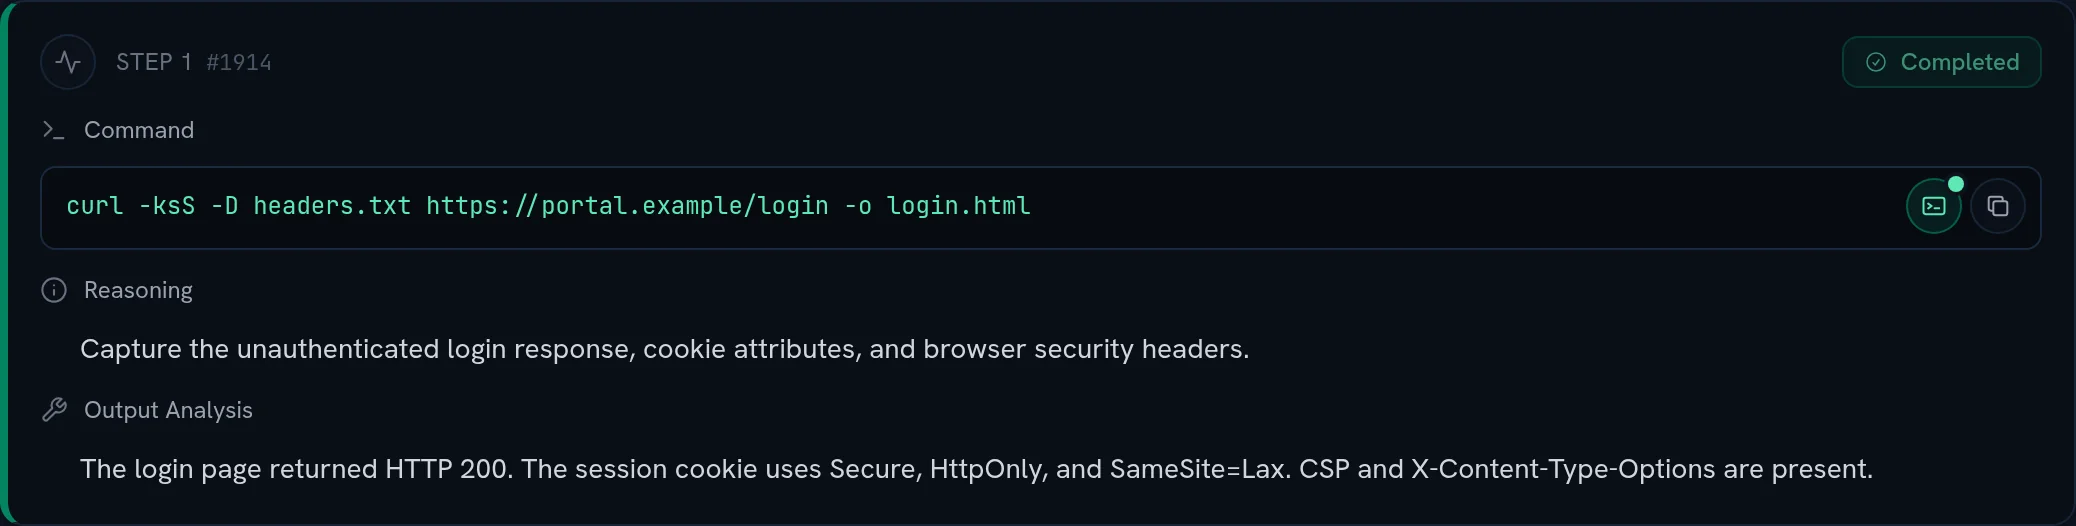
Sample data from an authorized lab environment. Every completed step is recorded in this same structure.
Tests execute on a dedicated Alpha.
An Alpha is an execution environment registered to your organization, typically a Kali machine. Zarb plans the work and maintains the record, while the Alpha runs the security tools against the target. You can pause the sequence, cancel a running step, and resume at any time.

Managed Alpha
We operate the environment
We provision and maintain a Kali Alpha for your organization and keep it connected to Zarb. Your only requirement is to allow its testing traffic to reach the systems in scope.
Customer-owned Alpha
You operate the environment
Register a machine you already run. Zarb connects to it over direct SSH, using credentials held against your organization and encrypted at rest.
Raw output stays attached to every step.
Each analysis is written from whatever the tool actually returned, and that output remains attached to the step. Very large responses are capped in the viewer. Any files created during the run stay on the Alpha and can be downloaded from the mission directory while it is online.

Re-run the same methodology on demand.
A scan applies a fixed methodology to the targets you declare. Once remediation is complete, clone the scan, run it again, and read the new report alongside the old one. Active scans can be paused and resumed.

What Zarb Delivers
Missions
A single objective, planned into reviewable steps before anything runs. The plan adapts as output comes back.
Campaigns
A larger goal split into missions that run in sequence, with the findings of each one carried into those that follow.
Scans
Hands-off web and network assessments against a fixed methodology and declared targets, with coverage that is measured rather than assumed.
Reports
Executive and detailed write-ups of every run, both downloadable as PDFs.
Measured Coverage, Not Assumed Completion
An agent that chooses its own next move can also choose to stop early, then produce a polished report that never states what was reached, what was tested, or why the run ended. Intelligence-driven testing is only worth trusting if completion can be measured.
Every scan in Zarb therefore maintains a coverage ledger. As the agent reports what it finds, including origins, endpoints, inputs, authentication states, and test classes, each item becomes a unit the platform tracks. Units that remain open trigger another bounded pass. If gaps persist after those passes, the scan still completes, but the report is required to declare what was missed.
Conditions the scan checks before completing
-
An API specification was found but not expanded
The next pass is instructed to account for the routes behind it.
-
Supplied credentials were never used
Authenticated testing is recorded as a gap rather than passed over.
-
The discovered inventory is unusually thin
The scan receives another bounded discovery pass.
-
Endpoints were reached but not inspected
They remain visible in the report as unfinished coverage.
Where the Boundaries Sit
Testing runs outside the control plane
Zarb plans the work and stores the record. The security tools themselves execute on an Alpha belonging to a single organization, whether we manage it or you connect it.
Tenant data is organization-scoped
Missions, campaigns, scans, and Alphas are all loaded through the current organization boundary, so no organization can read another.
Scans carry an explicit target boundary
Web scans use exact origins and network scans use declared hosts. Anything outside that boundary cannot enter the coverage ledger.
Operators retain control of execution
Regular missions wait for you to press Start. Active work can be paused, running steps can be cancelled, and every finding the agent records remains yours to review.
See Zarb Run Against Your Own Environment
Open the read-only demo account and explore a completed assessment on your own, or tell us what you test today and we will set your organization up with a walkthrough against a target you are authorized to test.